Open-source real-time packet analyzer uses Jev to classify anomalous traffic
The tool passively listens to Wi-Fi and pre-filters 99% of normal traffic, sending only anomalies to Jev for real-time classification, with a Redis queue and a FastAPI live dashboard; the author suggests a local model for sensitive networks.
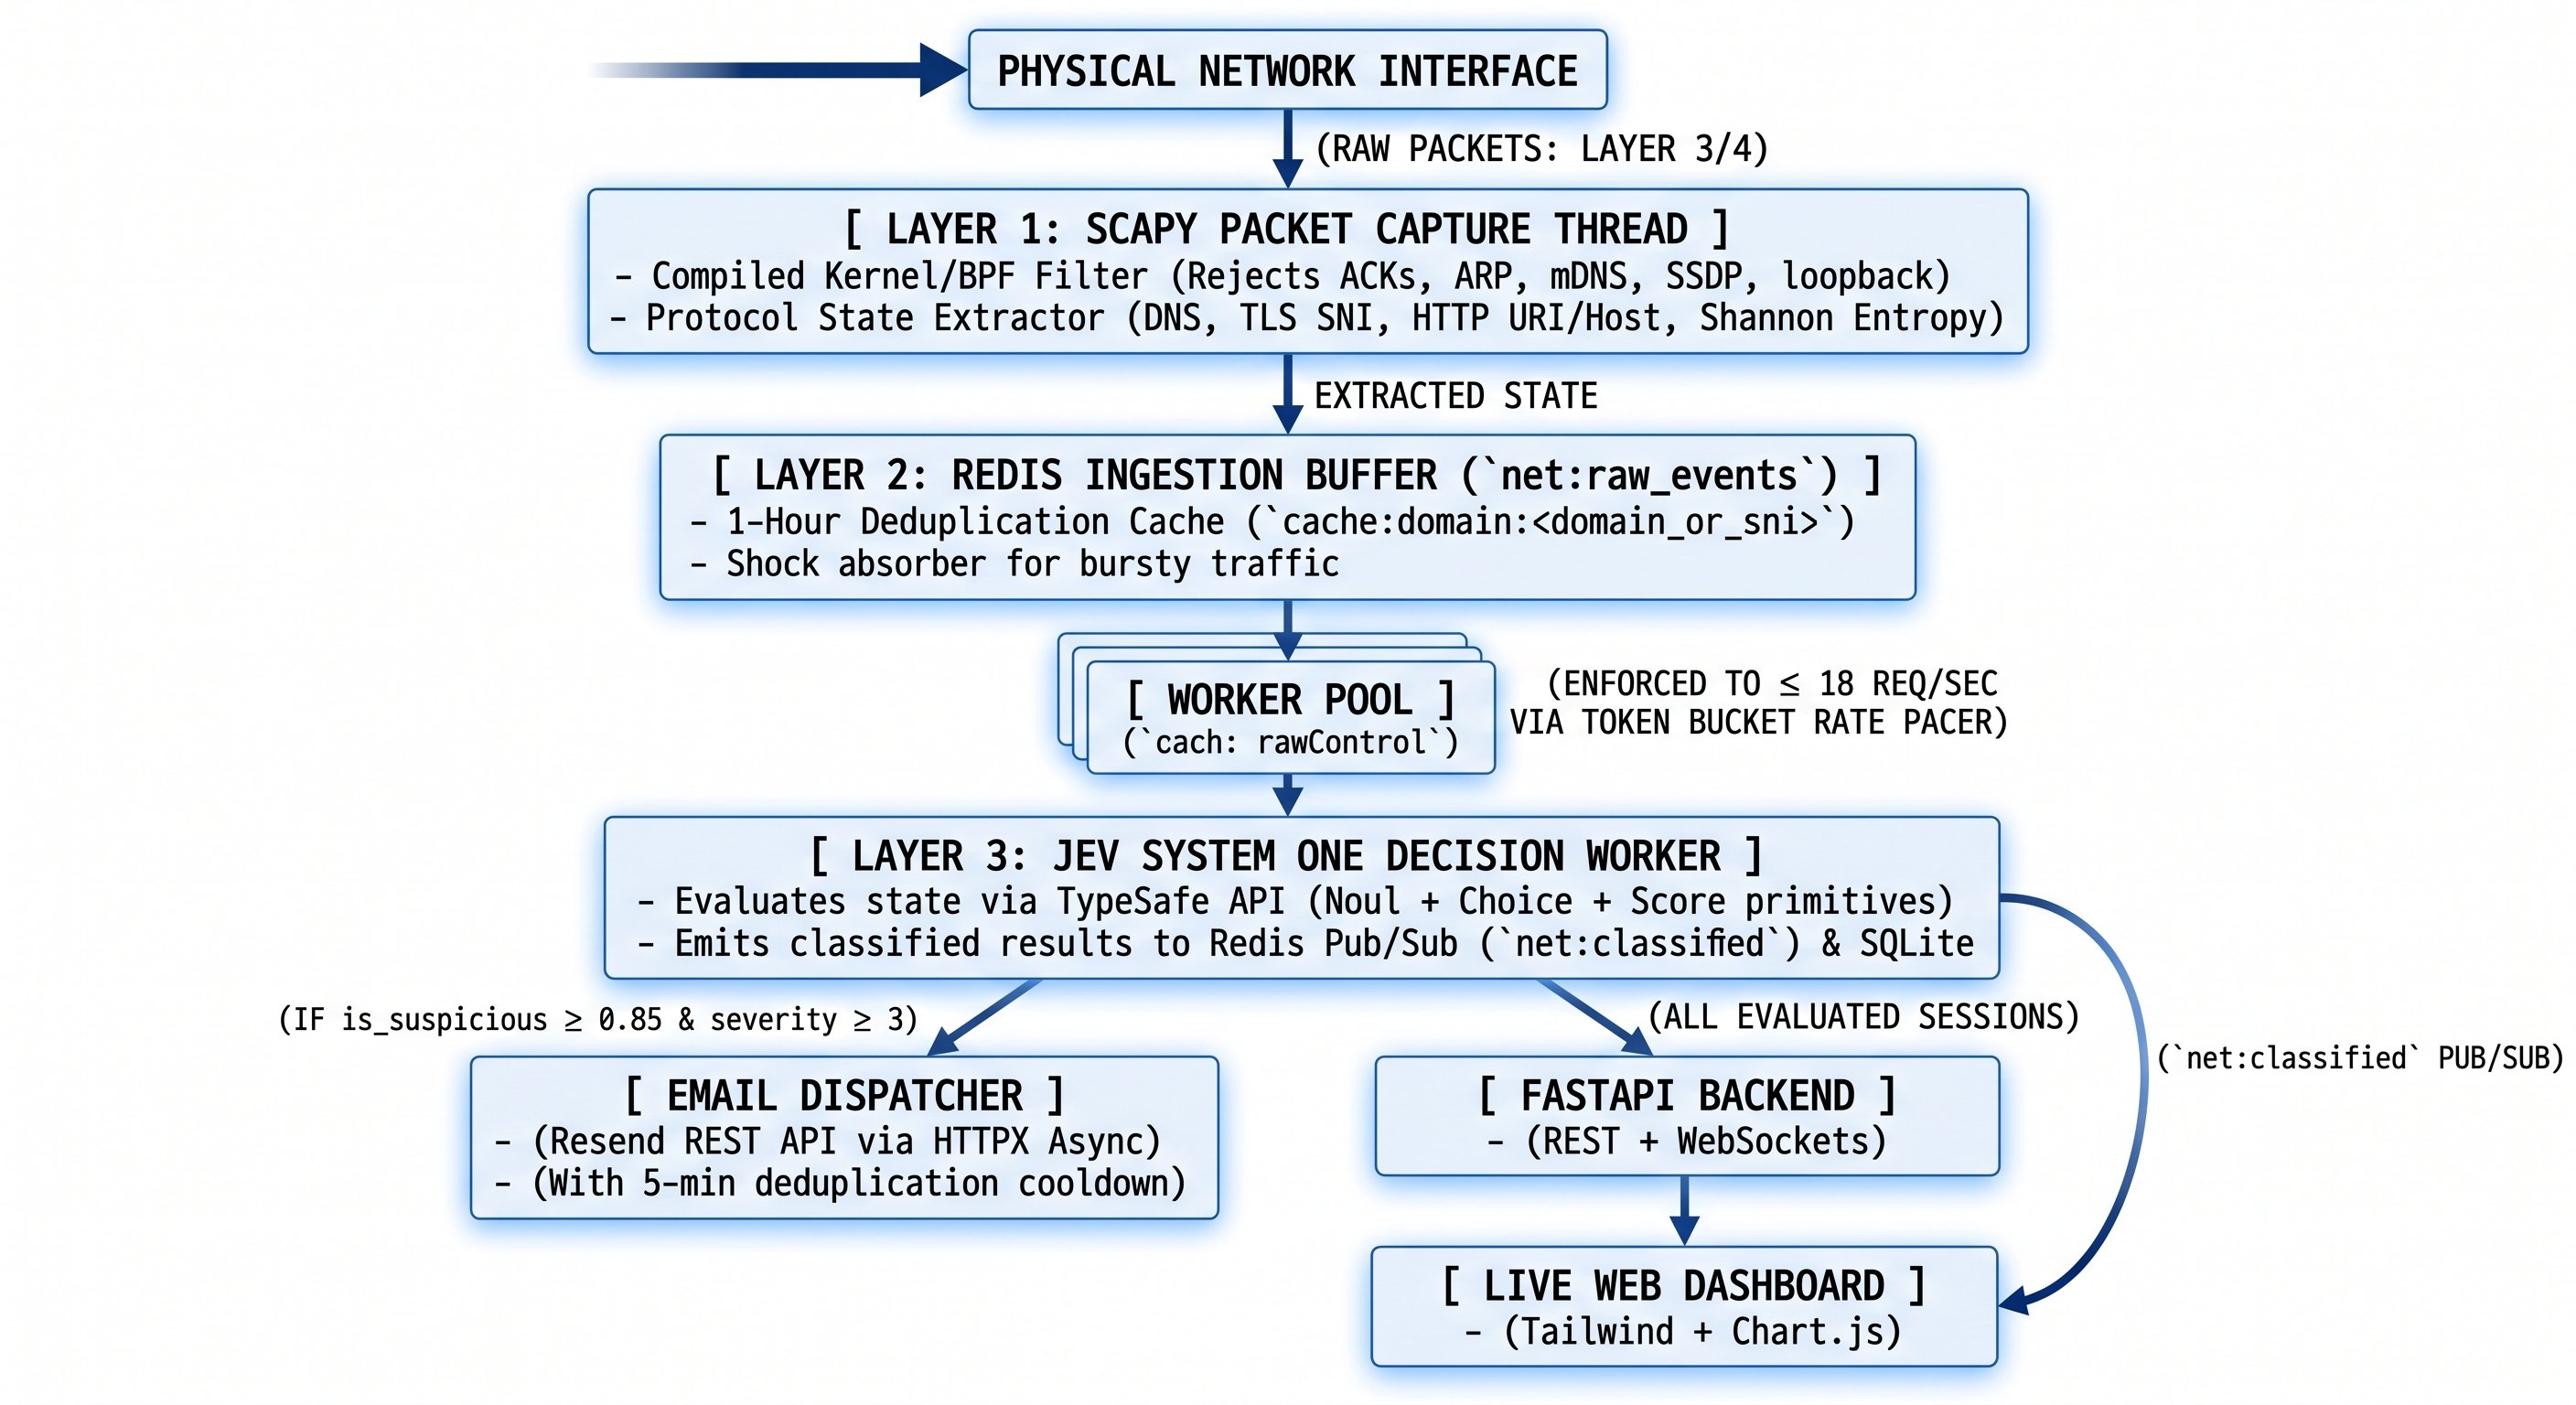
As promised.. The REAL-TIME network packet analyzer is officially open source! - Passively listens to your Wi-Fi, pre-filters out 99% of normal traffic - Only sends actual anomalies & suspicious payloads to @typesafeai's JEV to classify in real time - Buffers high-speed packet bursts in a Redis queue + bidirectional flow cache - Live cyber dashboard (FastAPI + WebSockets) - Instant email alerts via @resend 🧠 THOUGHTS & NEXT STEPS: - This is a fun PoC using JEV, but for sensitive private networks, the ideal next step is hooking this up to a local model (e.g. laya) so zero packet data ever leaves your LAN - I'm setting up an isolated test network soon to run simulated attacks and benchmark reliability DISCLAIMER: It's an experimental project, not production security software (use at your own risk!). Fork it, try it, and customize it! 👇 https://github.com/brainstormity/Jev-Network-Packet-Analyzer
This post quotes another post: “Jev packet classifier finds real backdoors on a family Wi-Fi network”