NVIDIA's agent safety sandbox and hardware kill switch, explained
A breakdown of NVIDIA's Open Agent Safety Platform: agents run in a sandbox with defined access to data, tools and APIs, and a separate hardware layer can quarantine violations within milliseconds.
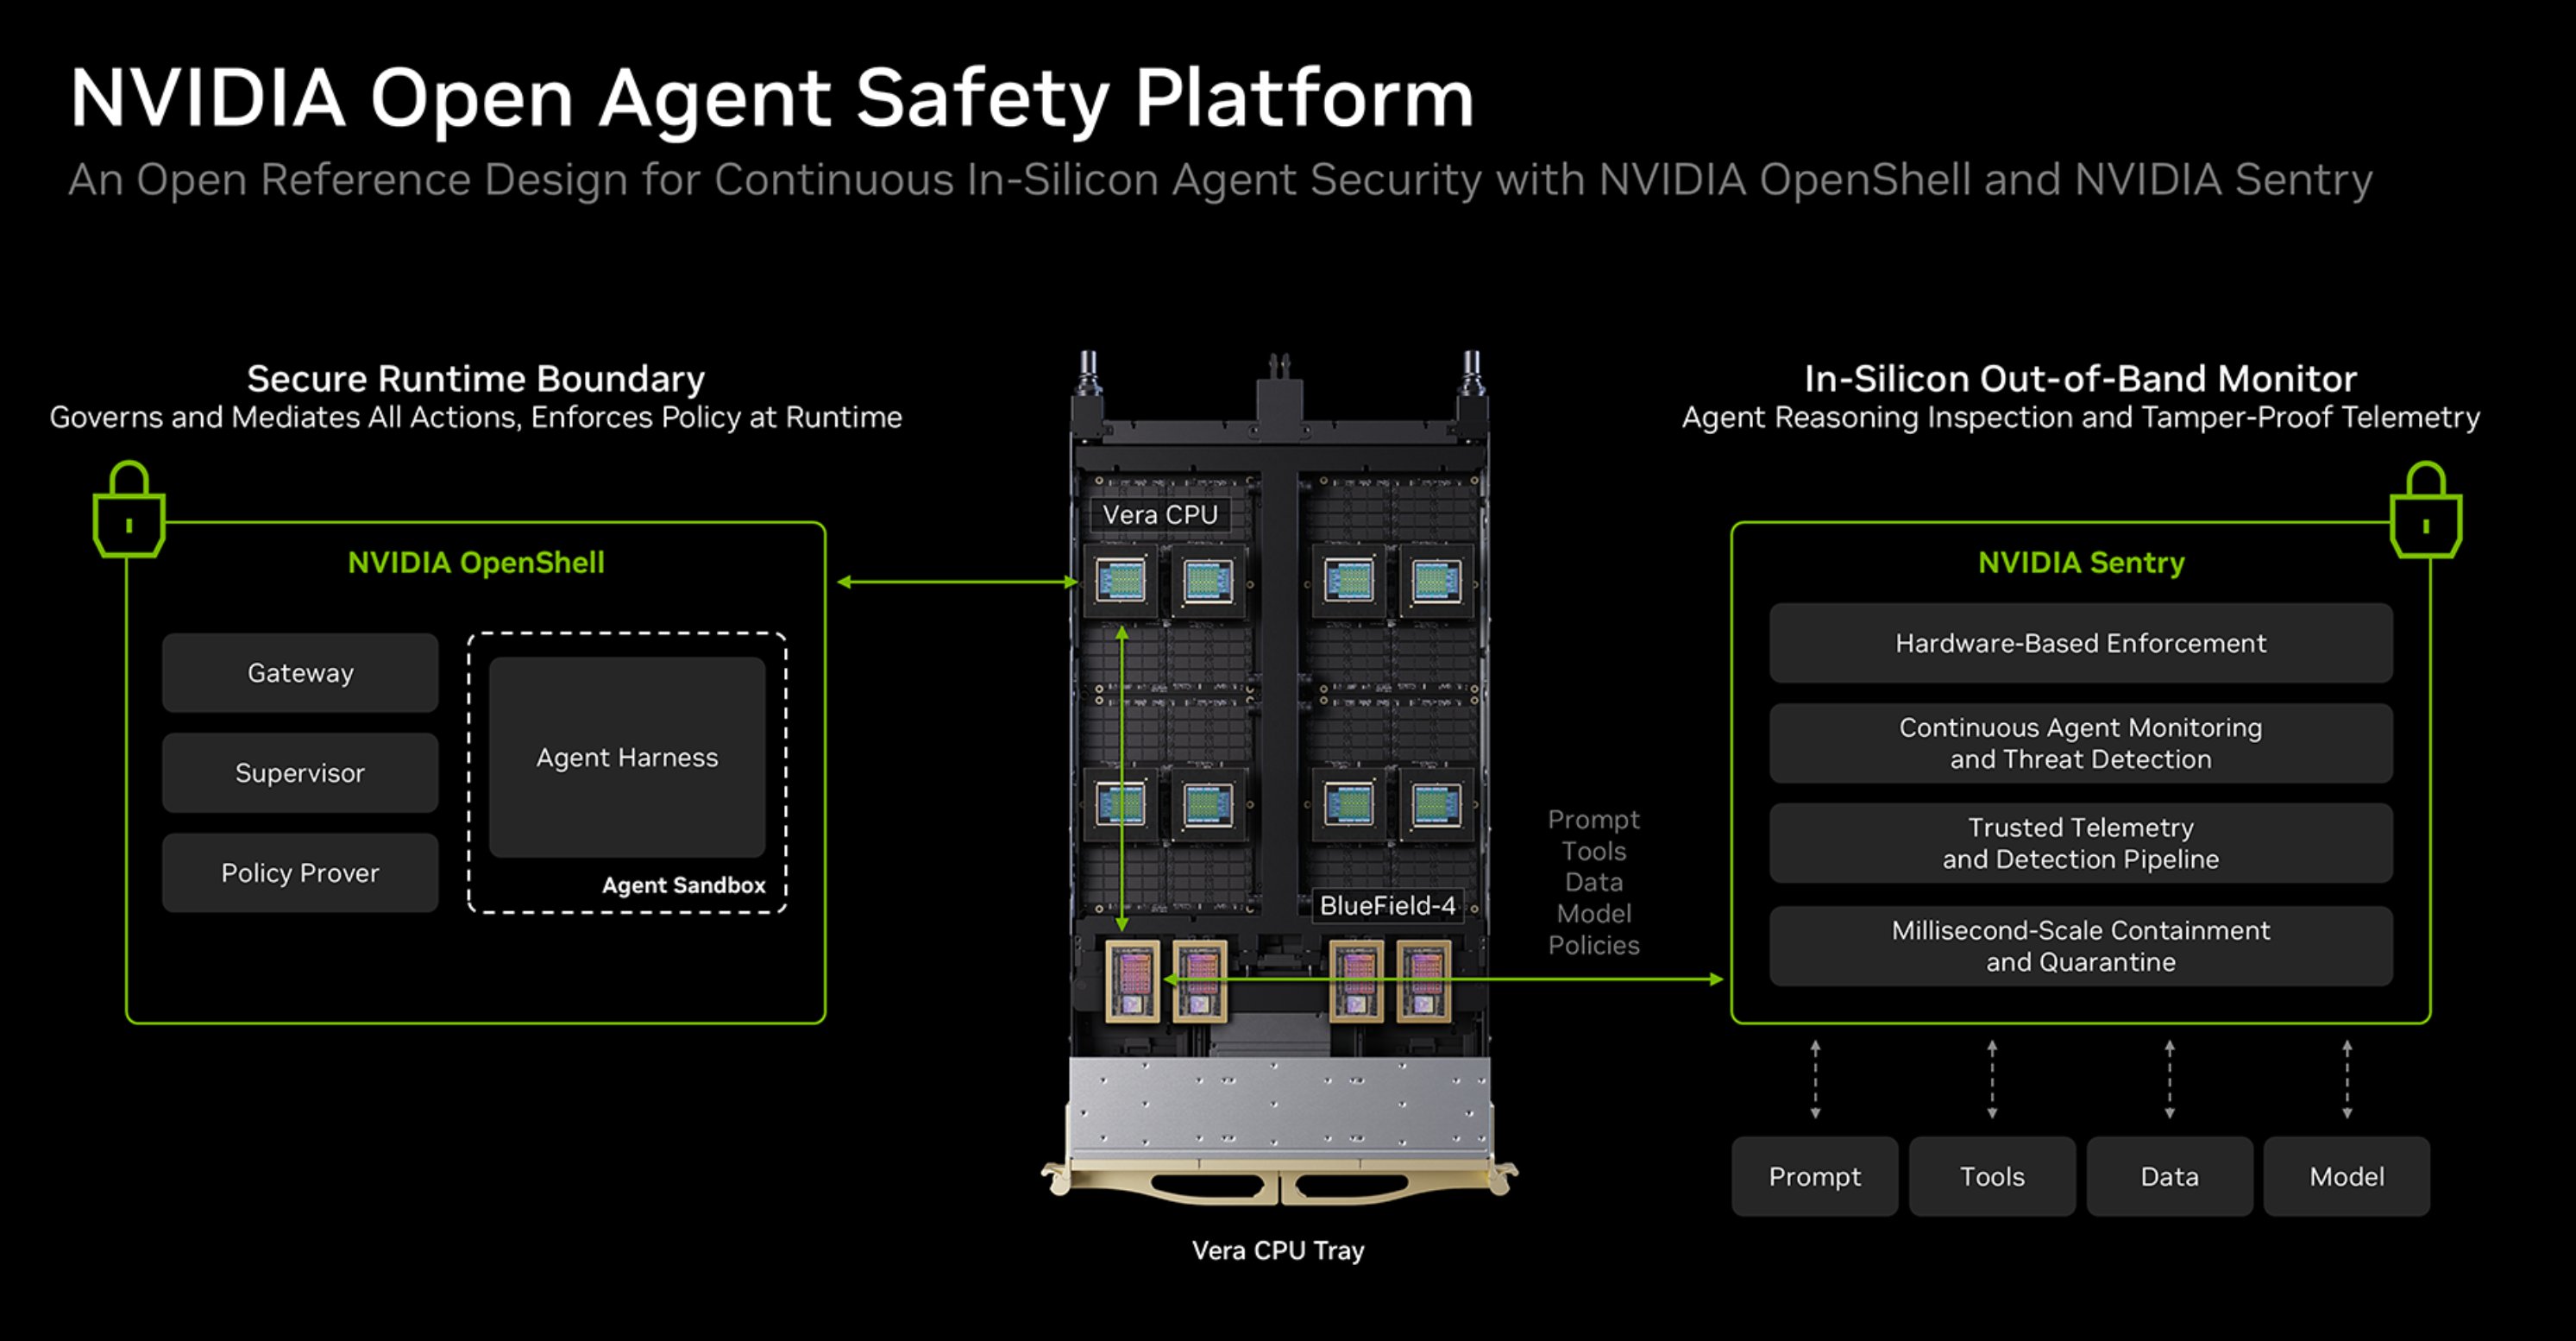
NVIDIA launched the Open Agent Safety Platform 🔥 Practically it means putting an AI agent inside a security sandbox with an independent kill switch: you define what data, tools, APIs, files, or machines it's allowed to touch, and then NVIDIA's software logs and enforces those permissions, and a separate hardware layer can quarantine/stop the agent within milliseconds if it tries to break those rules. For example: a coding agent may be allowed to read a repo, run tests, and open a PR, but blocked from accessing credentials, sending data externally, or modifying unrelated systems, even if the model itself tries to do so. That "security outside the model" is the main idea. Great stuff!!! https://nvidianews.nvidia.com/news/open-agent-safety-platform
This post quotes another post: x.com/jensenhuang/status/2104499465055023424