Meta 因漏洞报告为 Muse 加安全警告
安全研究员通过漏洞赏金报告 Muse 缺陷,攻击者或可访问用户专属云虚拟机;Meta 的回应是加强应用内警告而非打补丁。
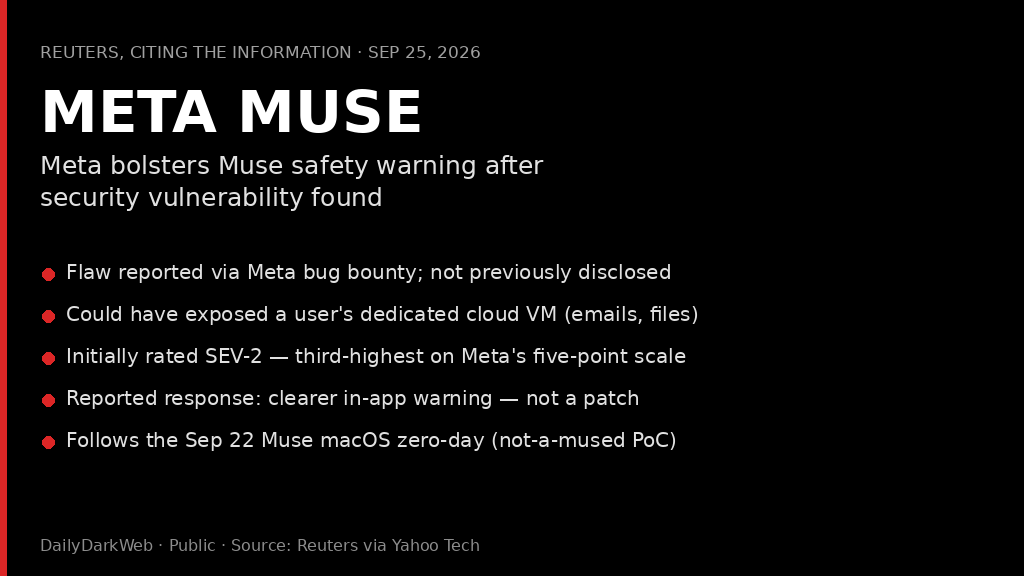
🚨 META ADDS STRONGER MUSE SAFETY WARNING AFTER NEW AI AGENT VULNERABILITY REPORT Meta Platforms is adding a clearer safety warning within its Muse AI agent after a security researcher found a vulnerability that could let an attacker access a user's sensitive personal information, Reuters reports, citing The Information. • The flaw was reported by an outside researcher through Meta's bug bounty program and had not previously been disclosed • Per an internal Meta incident report reviewed by The Information, it could have allowed an attacker to access a user's dedicated virtual machine — an individualized cloud-based account containing data including emails and files • Meta initially classified it as "SEV-2", its third-highest severity level on a five-point scale • Meta's reported response is a strengthened in-app warning, not a patch — the report does not say whether the underlying flaw has been fixed • Meta did not immediately respond to Reuters' request for comment • Muse, launched earlier this month, carries out tasks such as shopping, travel booking, emailing and payments on users' behalf ⚠️ Analyst Note: This follows the Muse macOS zero-day we covered on Sep 22 — Patrick Wardle's not-a-mused PoC, which abused an undocumented dictation-endpoint setting and required existing local code execution. The newly reported bug-bounty flaw concerns access to users' cloud virtual machines; the report does not link it to Wardle's bug, so treat them as separate issues. Two security problems in Muse's first month underline the risk of AI agents holding broad access to email, files and payments. Source (Reuters, citing The Information, 25 Sep 2026): https://tech.yahoo.com/ai/meta-ai/articles/meta-bolsters-muse-safety-warning-181523688.html Earlier zero-day PoC (Patrick Wardle): https://github.com/pwardle/not-a-mused Our Sep 22 coverage: https://x.com/DailyDarkWeb/status/2102271029942890616 #DDW #Meta #Muse #AISecurity #AgenticAI #ThreatIntel #CyberSecurity #DarkWeb
这条是引用着另一条写的:「Meta Muse macOS 本地零日漏洞 PoC 公开」