PHP 补丁提前泄露事件:Gemini 4 Argon 也发现了同一漏洞
PHP 补丁原定 10 月 22 日发布,却提前泄露,NSA 也罕见地发布公告;帖主称 Gemini 4 Argon 与 OpenAI 系统各自独立发现了同一漏洞。
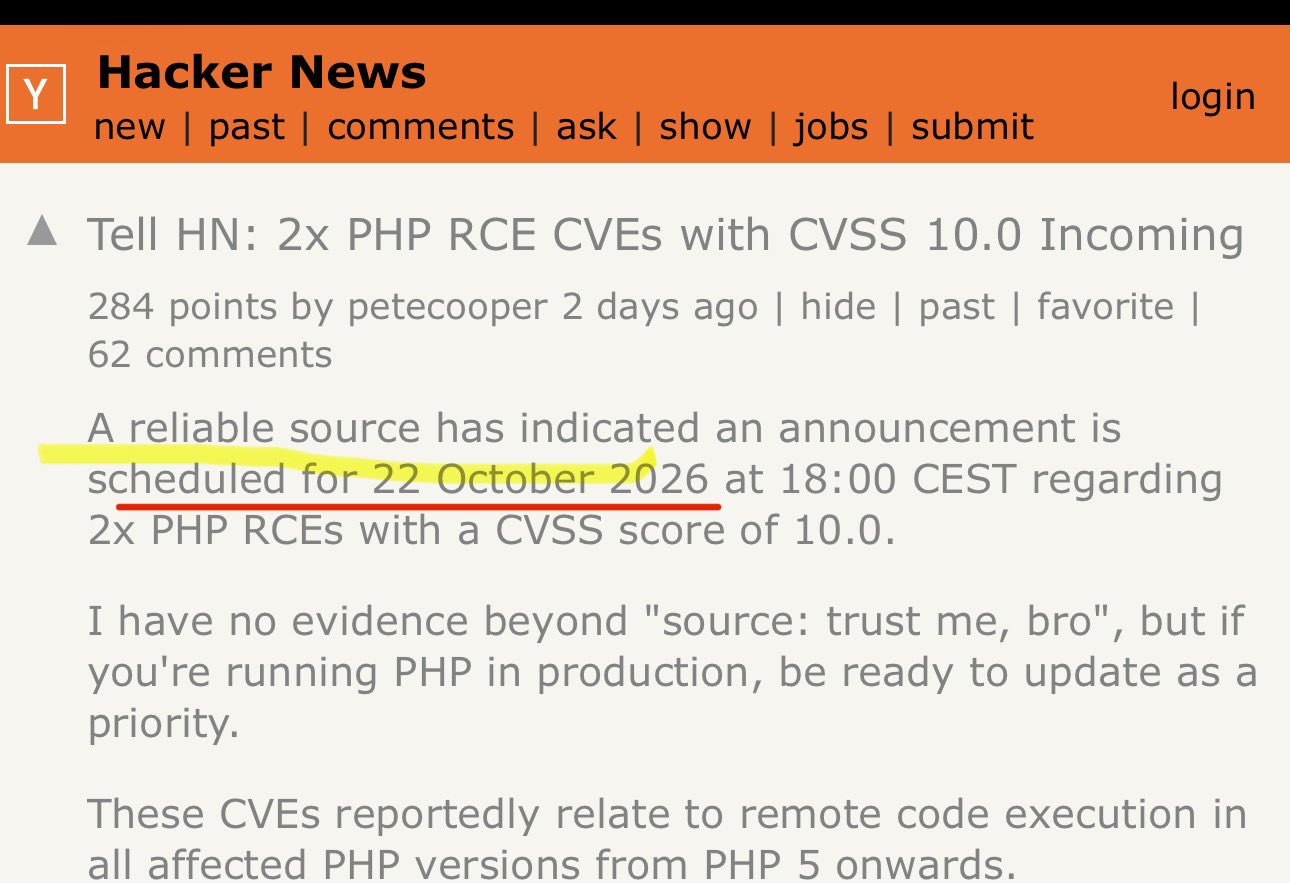
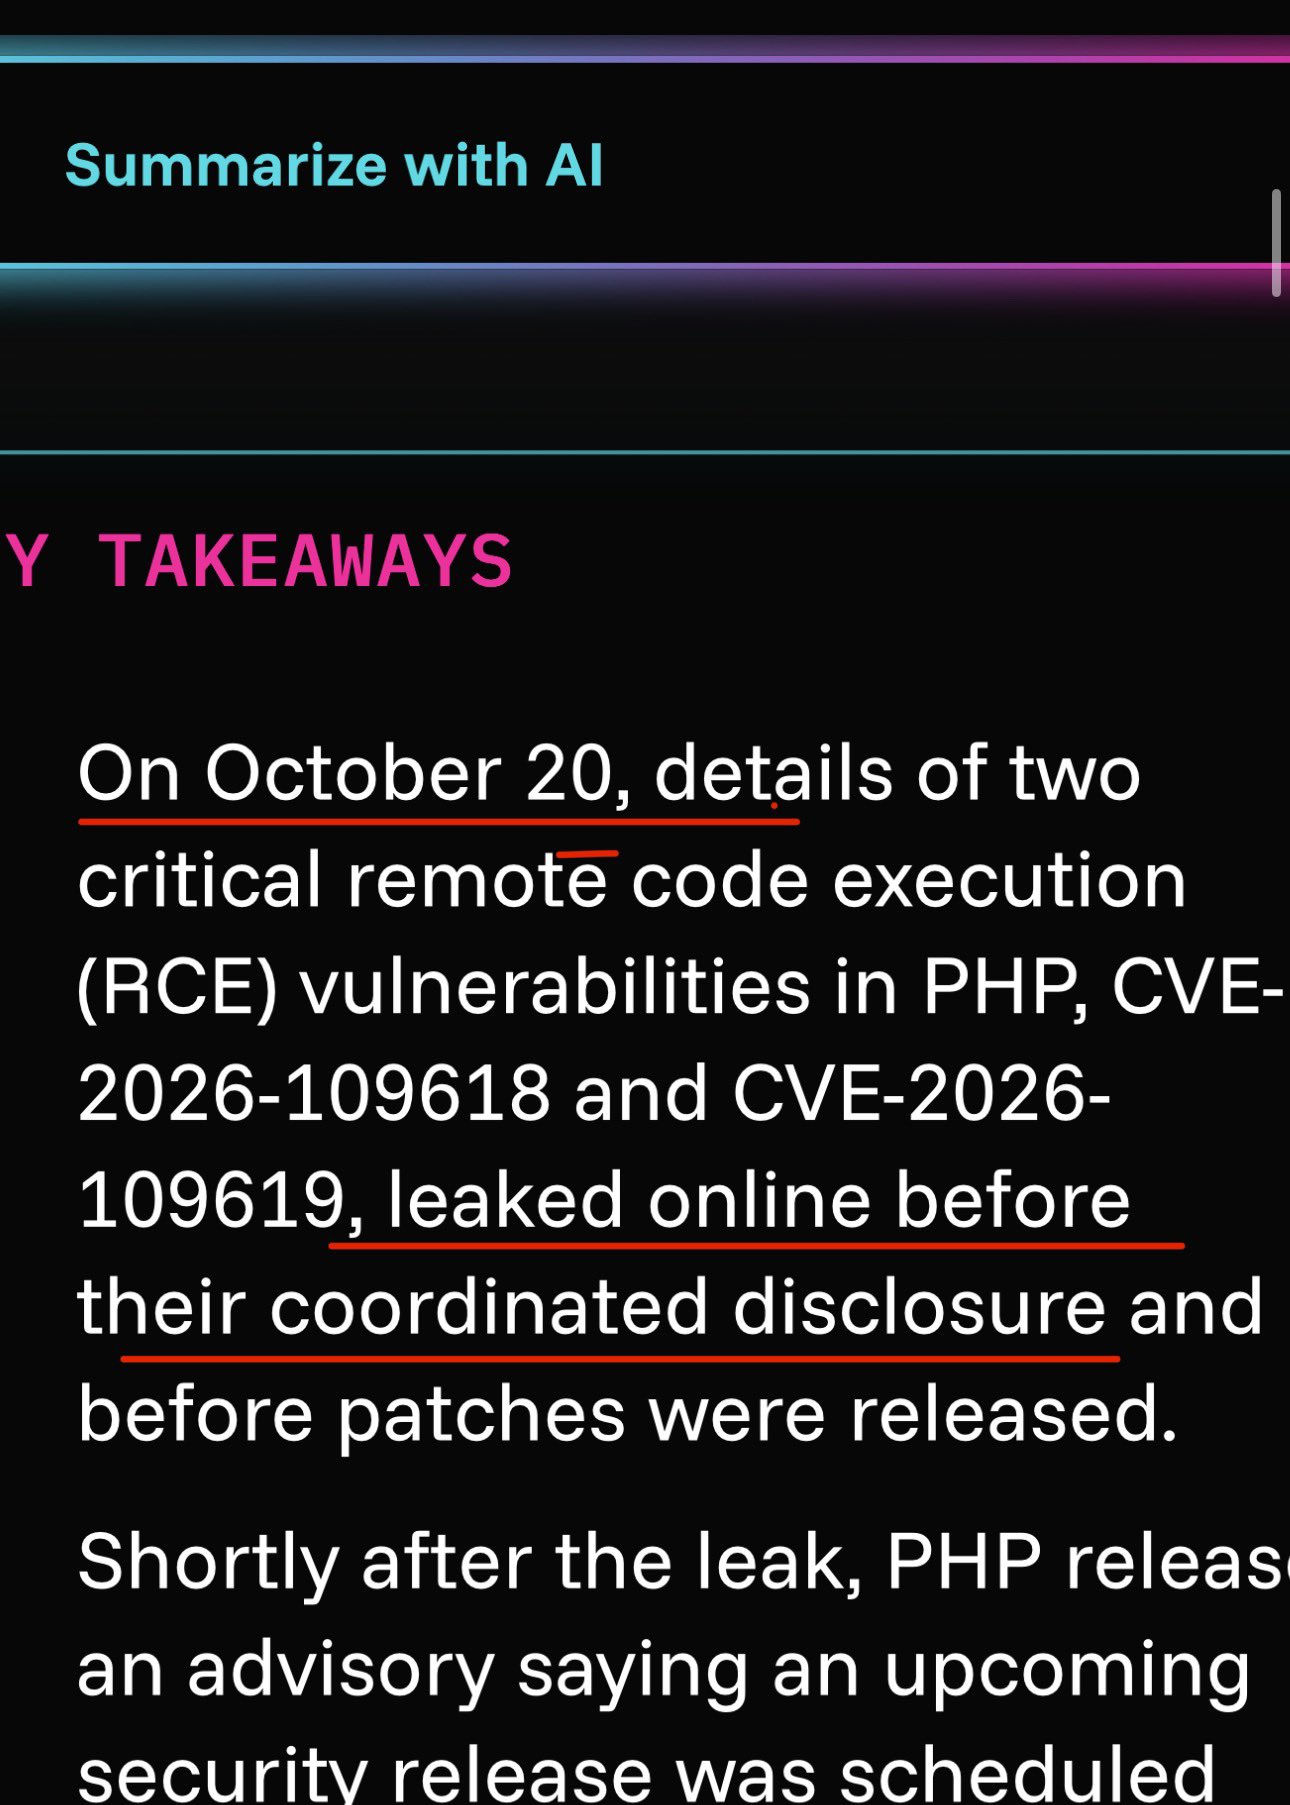
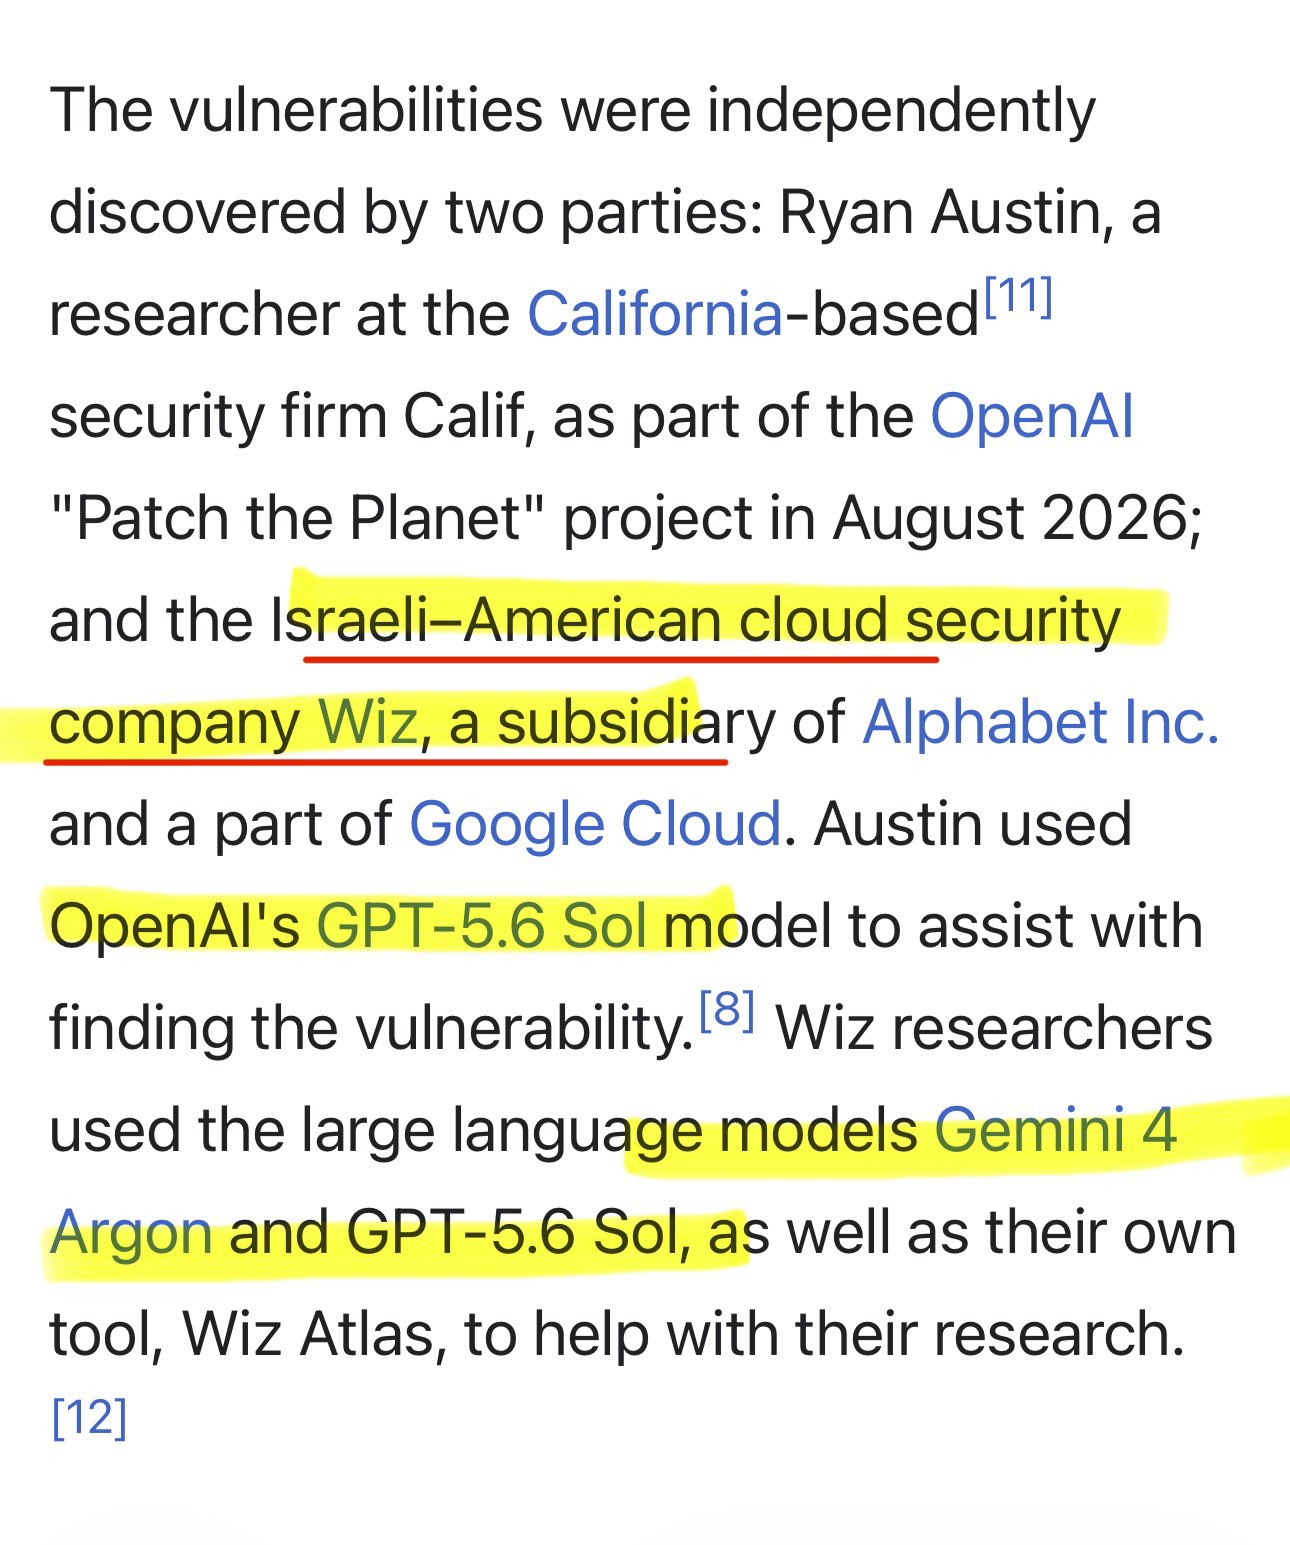
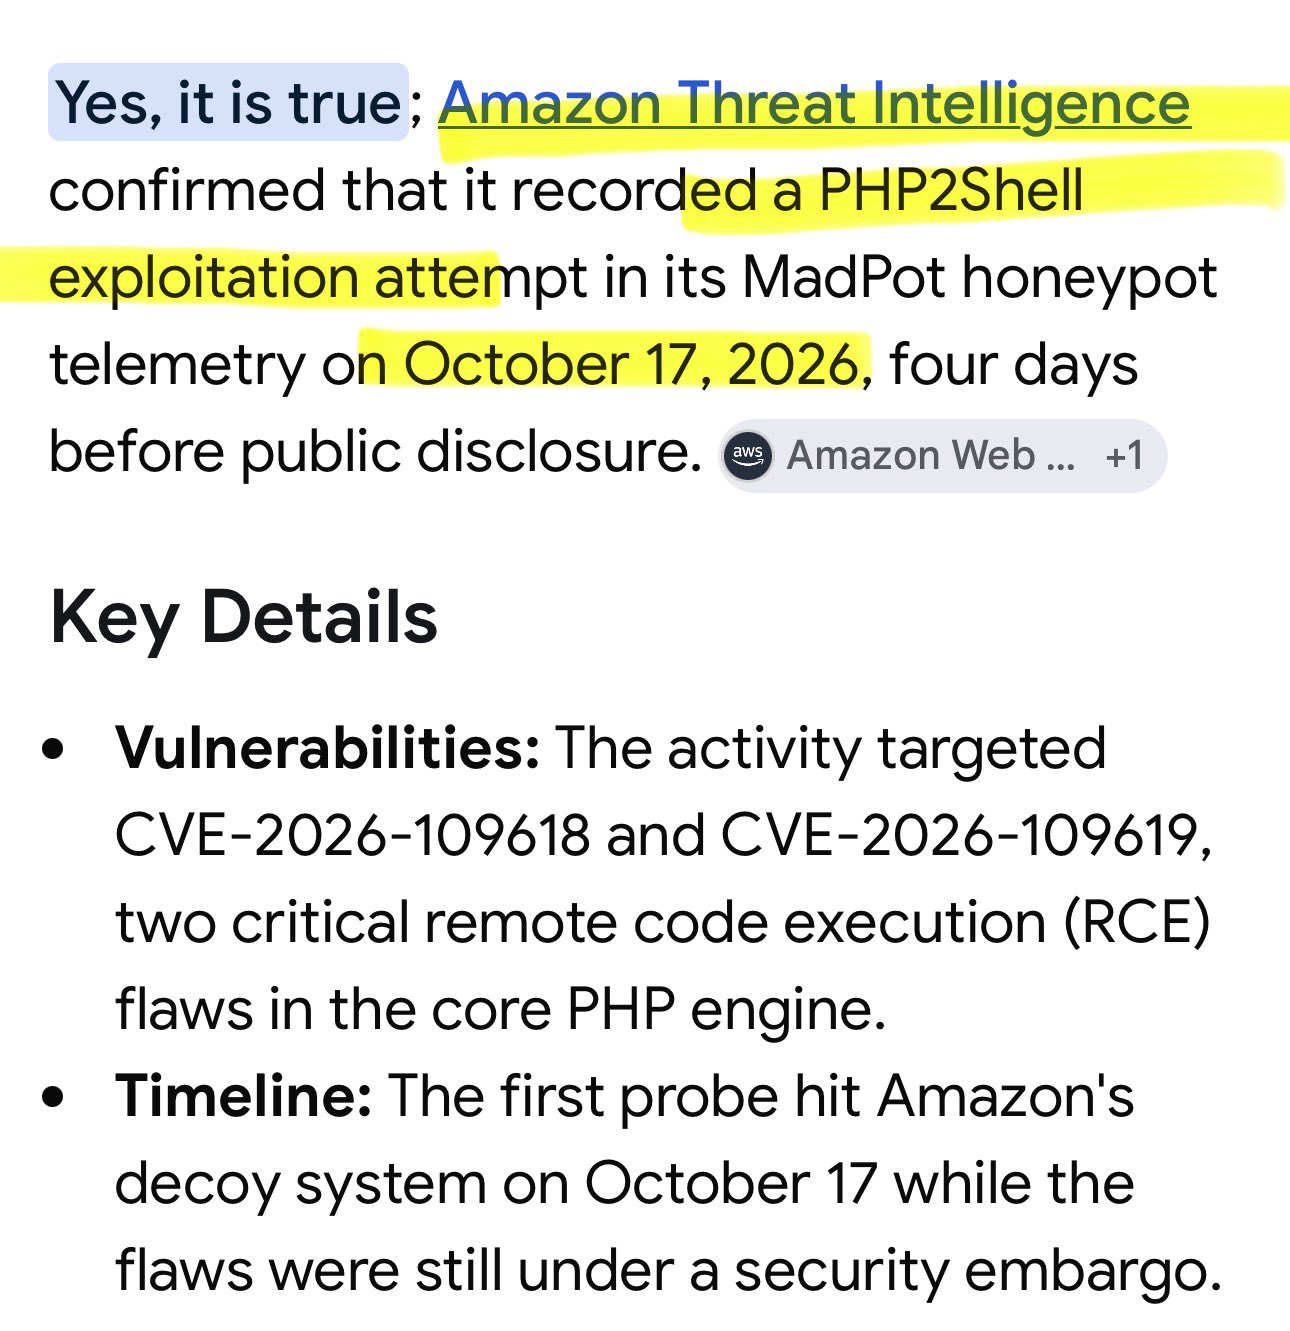
the patch was supposed to release on October 22nd, ⚠️but someone leaked it early on October 20th, and then the NSA released their advisory. The coordinated disclosure was planned for Thursday, October 22 Someone leaked details on October 20 (two days early) PHP moved the patch to October 21 (one day earlier than even the moved date) NSA released advisory on October 21 👀👀🚨🚨 The NSA didn't wait for the official patch to be released before publishing their advisory. They were ready to go the moment the leak happened.🚨 This means the NSA already had the advisory written before the leak. They were prepared. They knew about this vulnerability before the public discovery. 🚨 Not only this The NSA typically doesn't issue public advisories about PHP vulnerabilities. They focus on classified systems.🚨 The fact that they're issuing a public advisory about a web vulnerability suggests they're using this as a pretext for something larger. Someone who was part of the coordinated disclosure process leaked the details to force the PHP team to release the patch early. This person wanted the patch out before the original Thursday embargo.🚨 Whats even more unusual is that Gemini 4 Argon found it too. This means multiple AI systems (OpenAI's Patch the Planet and Google's Gemini 4 Argon) independently found the same vulnerability. 🚨 Wiz is a subsidiary of Alphabet Inc., which is Google. Now look at the overlap. Calif used OpenAI's GPT-5.6 Sol. But Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating back to October 17, 2026, four days before public disclosure. This means a hostile actor had already found and was exploiting the vulnerability before the "independent discovery" was publicly announced. The intelligence community likely detected this exploitation through signals intelligence or threat hunting. They realized the bug was burned. A hostile actor was already in.🚨👀 Intelligence services (likely the NSA, given their rapid response) had this exploit in their library. AI vulnerability scanners were getting close to finding it independently. To prevent a hostile intelligence service from finding it first and weaponizing it, the NSA and allied intelligence services coordinated a controlled burn operation. 🚨👀 Imo they used Google (Wiz) and OpenAI (Calif) as cutouts to create the appearance of independent discovery. This provides cover for the intelligence community: "AI found it, we didn't hoard it, we're just responding to a new discovery." 🚨👀Basically the era of intelligence services hoarding vulnerabilities is over. AI is finding them all. This PHP vulnerability is the first public casualty of the AI-driven vulnerability discovery race. https://www.huntress.com/blog/php2shell-leaked-critical-php-vulnerabilities https://www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Release-View/Article/4630238/nsa-advisory-critical-patches-recommended-for-php-vulnerabilities/ https://www.aikido.dev/blog/critical-vulnerabilities-in-php-php2shell