把 Jev 当 agent 工具调用的放行闸门
提议在 agent 调用 MCP/API/数据库前插入 Jev 评估:ALLOW / BLOCK / ESCALATE,LLM 决定想做什么,Jev 决定允许做什么。
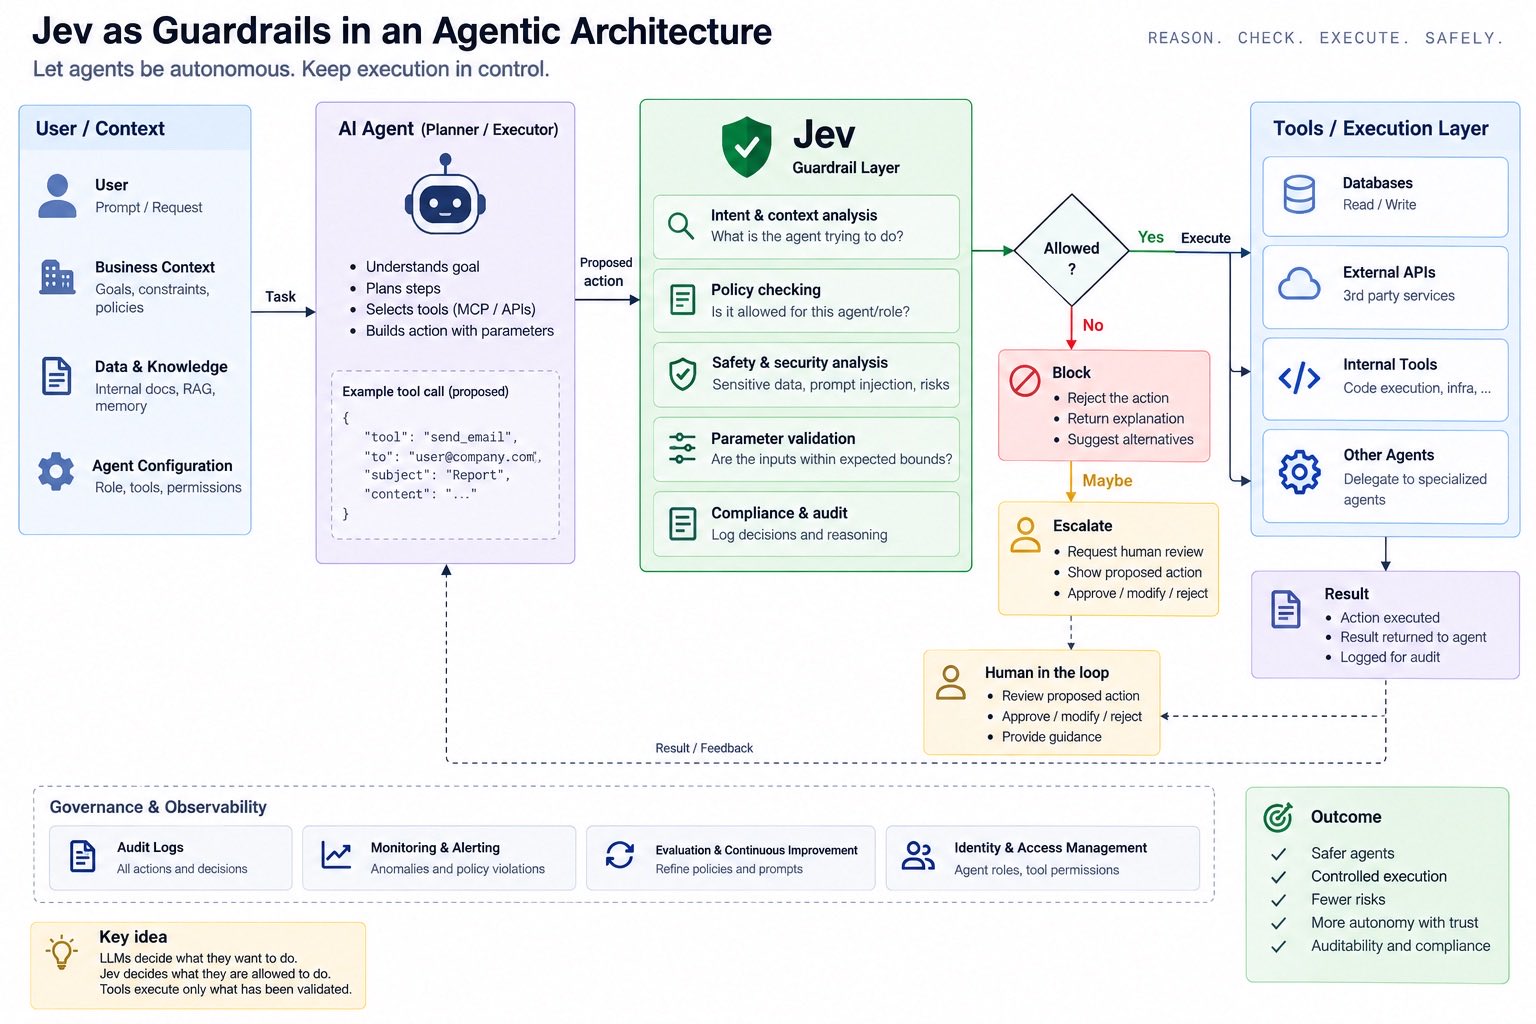
Could Jev become a guardrail layer for agentic architectures? The more autonomy we give agents, the more I think the real question shifts from: “Can the agent do this?” to: “Should we allow the agent to do this?” Imagine the flow: Agent reasons → proposes an action → Jev evaluates it → ALLOW / BLOCK / ESCALATE → Tool executes. Before a tool call reaches an MCP server, API, database or another agent, Jev could potentially evaluate: → Is this agent allowed to use this tool? → Is the action consistent with its original task? → Are the parameters within expected boundaries? → Is sensitive data involved? → Does this action require human approval? → Is the agent deviating from the expected workflow? That would create an interesting separation: LLMs decide what they want to do. Jev decides what they are allowed to do. Tools execute what has been validated. Could this become a practical security/control pattern for agentic systems? Curious to hear how others see Jev fitting into this architecture.