Grok Bot memory sharing risk and a safer setup
xAI docs show all Grok Bots on one account share a single cloud computer with files and logins; the post proposes narrow roles, file handoffs and human approval.
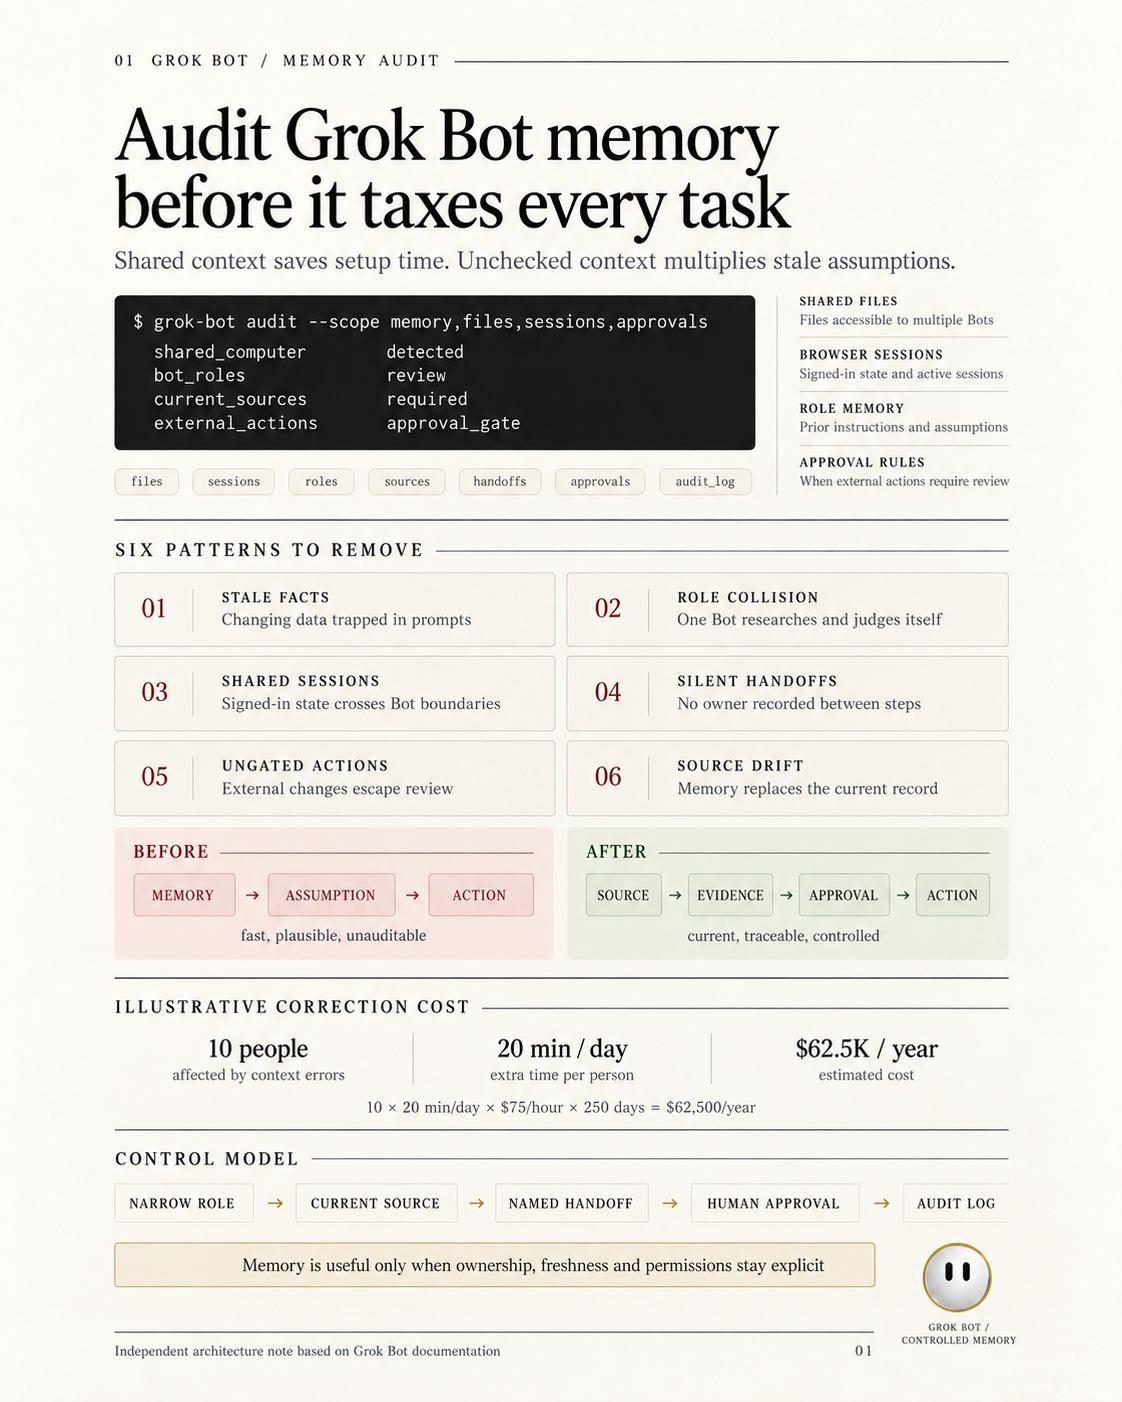
Your Grok Bot may be getting worse because it remembers too much of the wrong thing xAI’s docs reveal a boundary most teams will miss: every Bot keeps its own role and conversation, but all Bots on your account share one cloud computer, including files, browser sessions and logins. Memory is not a security boundary. The reliable setup: > keep changing facts in source systems > give each Bot one narrow role > pass work through named files > require approval before sending, buying or deleting > reopen the current source for consequential decisions Then audit one week of corrections. If 10 employees lose 20 minutes daily fixing stale context at $75/hour, this reaches $62,500 a year. Larger memory will not solve it. The advantage comes from knowing who owns each decision, which source proves it and which actions still require a human.
This post quotes another post: x.com/pixu_alpha/status/2112190619321852076