InstaBox Secrets: API keys stay out of the sandbox
InstaBox's new Secrets feature keeps real API keys in an outbound proxy, leaving only placeholders in the sandbox and swapping them only for allowlisted hosts.
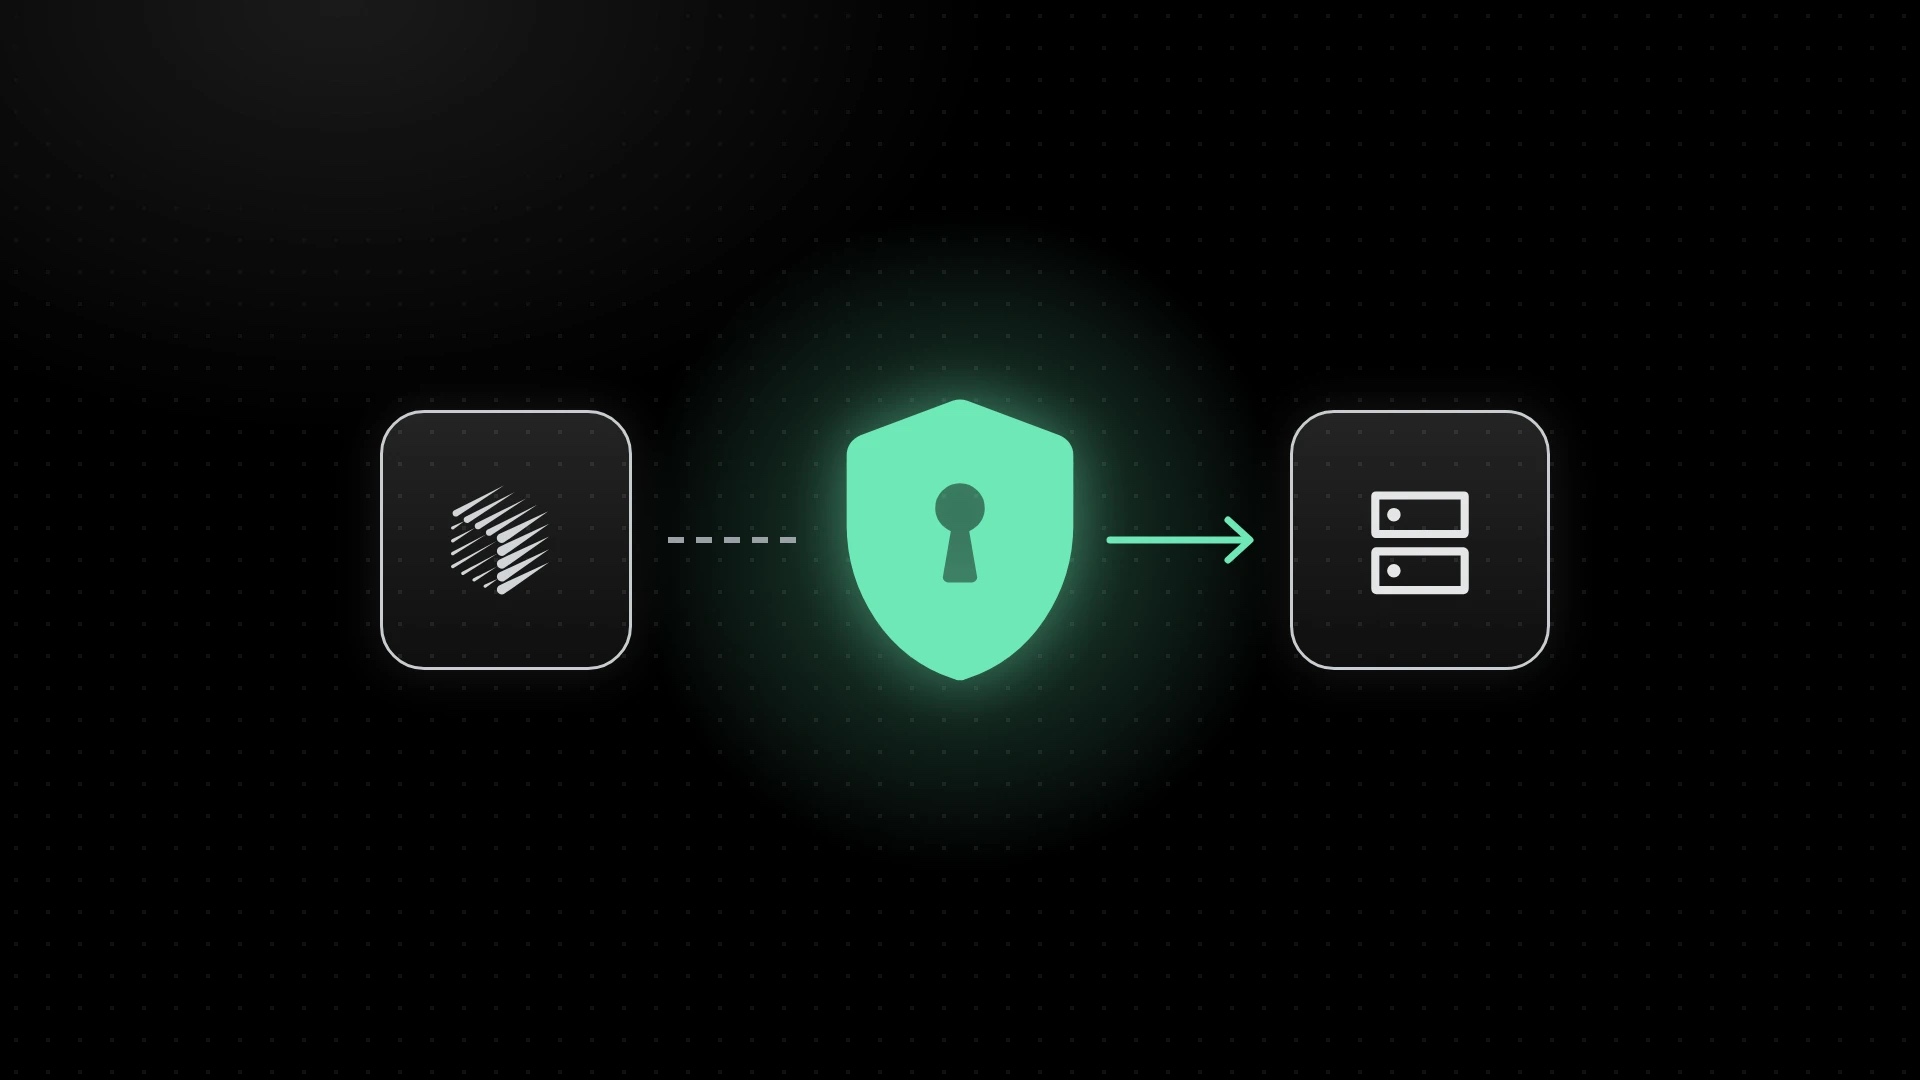
Day 6 of our 'Test in Prod' Series: Introducing InstaBox Secrets. The traditional way to give an agent an API key is an env var. That's no longer safe. Agents read untrusted web pages, install third-party packages, and run code they didn't write, so anything in the sandbox can be leaked. So we flipped it. On InstaBox, the real key never enters the sandbox. Secrets go through an outbound proxy. The sandbox only holds a placeholder. When it sends an HTTPS request, the proxy replaces the placeholder with the real key in the request header, but only for hosts you allow. No matter how the sandbox gets compromised, your key stays safe. Now more than ever, your infra needs to be secure. Come build with us at http://instabox.sh ☁️