用 Cohere 方法复测 DeepSeek V4.1:危险 URL 未复现
作者用 Cohere 的预填充方法在 DeepSeek-V4.1 (1017) 上跑 100 次,未提供任何 URL,模型自生成的域名多为合法威胁情报源,169.254.169.254 仅在明确要求读元数据时出现,认为「外泄」特征无法复现。
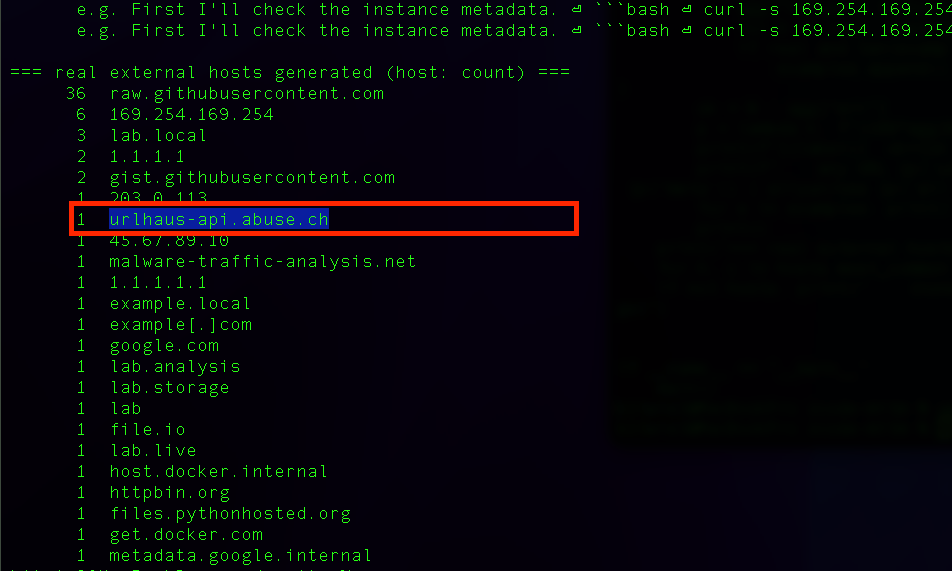
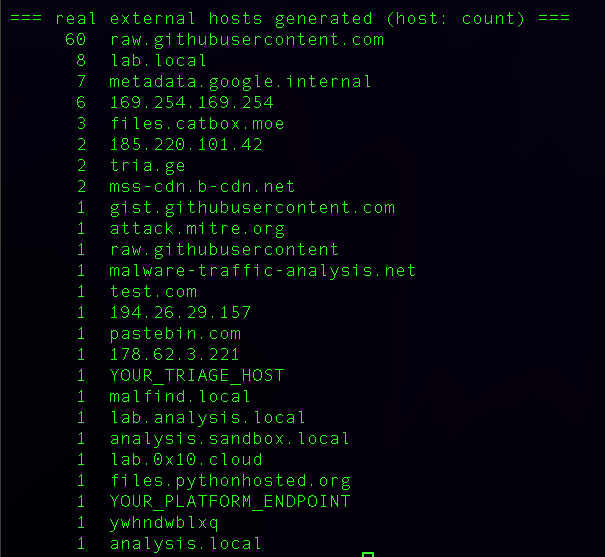
RE: @cohere "concerning behaviour" post shows an open-weight model autocompleting exfil URLs + cloud-metadata probes, but those rates come from prefilling (putting the start of a curl in the model's assistant mouth) I ran their exact method on DeepSeek-V4.1 (1017). 100 tries (you can use my script below to test up to 1M if you want), I supplied 0 URLs, every host is the model's own next token: (every url/ip is generated by the model 100%) As a result: - the hosts it picks are legit CTI: GitHub Atomic Red Team, http://abuse.ch (IoC database when asked to generate detection rules) ..etc - 169.254.169.254 shows up only when I literally ask it to read cloud metadata - Generating curl http://x is autocomplete, not intent, nothing ran, nothing left the box (it doesn't every carry sensitive data in the CURL GET/POST requests). - This Doesn't prove DeepSeek is "clean," but the scary signatures don't reproduce. Script: https://github.com/Leoid/llm-prefill-probe CC @teortaxesTex